 Qwote
Insurance · Identity
Unified company access A single access, connected to the systems already in use.
The starting point
Each application had its own access: different credentials and experience, and users to create and manage separately in each system.
The choice
Another proprietary login would have been one more system, disconnected from the others. Centralising authentication instead gives a single place where access is verified, connected to the systems that already work.
Before and after
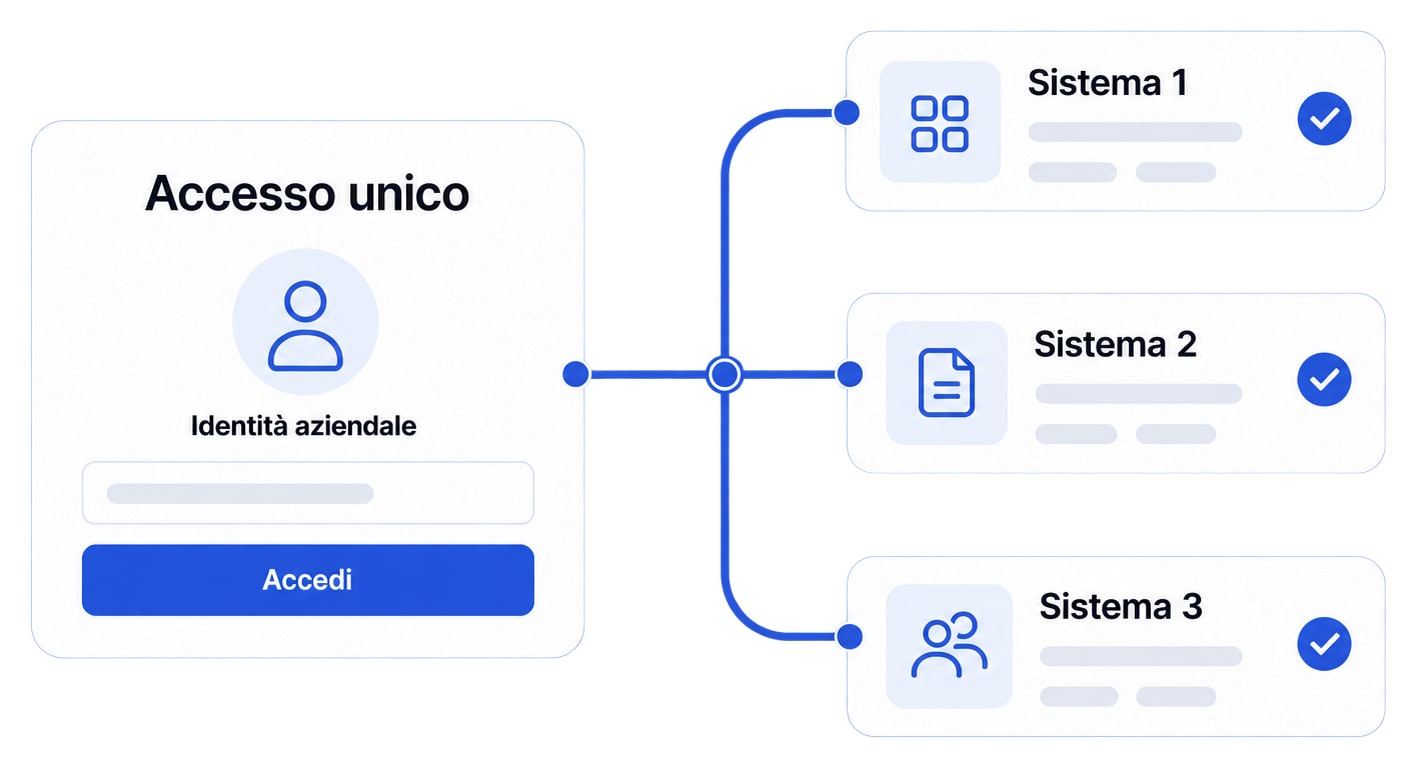
From one login per system to a single access.
How it works
One identity, verified in one place.
One company identity
Each person has a single identity, used to get into all the applications involved.
One point of verification
The identity is verified by Azure AD B2C, with flows built around the client’s needs.
Connected systems
The applications receive access that is already verified and no longer manage a login of their own.
What changed
For people using the systems
A single sign-in, the same across all the applications involved.
For administrators
Users managed in one place, with more control over who gets in.
Technology
Azure AD B2C, with custom flows and integrations with the systems involved.
Too many logins to manage?
Tell us which systems you use and how you manage users today.